

Inprosec a través de sus servicios, como el SAP Security Assessment, ayuda a sus clientes a mejorar los niveles de seguridad de sus sistemas SAP.
Notas noviembre 2026
Resumen y highlights del Mes
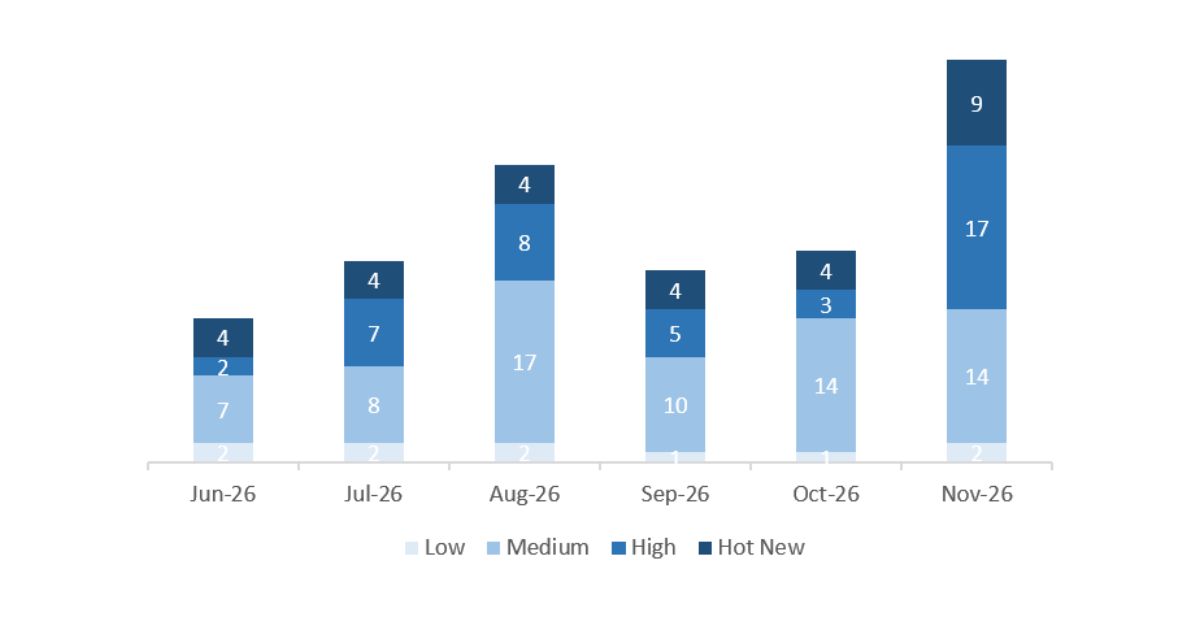
Este mes el número total ha sido de 42 notas (35 nuevas, 4 avisos de seguridad y 3 actualizaciones), 20 más que en octubre. Este mes se han publicado 9 Hot News, cinco más que en el periodo anterior. En cuanto a notas de criticidad alta, hay 17 (13 Notas SAP y 4 avisos de GitHub), catorce más con respecto a octubre. Las notas medias y bajas no serán revisadas. Además, para evitar confusión, hemos excluido del detalle los 4 avisos de GitHub, por lo que daremos detalle de un total de 22 notas (centrándonos exclusivamente en las Notas SAP puras con un CVSS de 7 o mayor).
Tenemos un total de 42 notas para todo el mes (35 nuevas, 4 avisos de seguridad y 3 actualizaciones de notas de meses anteriores).
Revisaremos en detalle un total de 22 notas, todas de criticidad alta y Hot News:
-
La nota más alta en criticidad del mes (CVSS 10,0) es una Hot News y está relacionada con “Memory Corruption Vulnerability in SAP NetWeaver AS ABAP (Internet Communication Manager)”.
-
La segunda nota con la misma criticidad (CVSS 10,0) es otra Hot News y está relacionada con “Memory Corruption vulnerability in SAP Web Dispatcher”.
-
La tercera nota con la misma criticidad (CVSS 10,0) es otra Hot News y está relacionada con “Broken Access Control in SAP Gateway”.
-
La cuarta nota con la misma criticidad (CVSS 10,0) es otra Hot News y está relacionada con “Missing Authentication in SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider)”.
-
La quinta nota en criticidad (CVSS 9,9) es otra Hot News y está relacionada con “Code Injection vulnerability in SAP NetWeaver Knowledge Management (XML Forms)”.
-
La sexta nota con la misma criticidad (CVSS 9,9) es otra Hot News y está relacionada con “OS Command Injection vulnerability in ABAP Application Server for SAP NetWeaver and ABAP Platform”.
-
La séptima nota con la misma criticidad (CVSS 9,9) es otra Hot News y está relacionada con “Missing authorization check in S4CRM”.
-
La octava nota en criticidad (CVSS 9,6) es otra Hot News y está relacionada con “Cross-Site Request Forgery (CSRF) vulnerability in SAP Web Dispatcher and Internet Communication Manager”.
-
La novena nota en criticidad (CVSS 9,1) es la última Hot News del mes y está relacionada con “XML External Entity (XXE) Vulnerability in SAP BusinessObjects Business Intelligence Platform (Web Intelligence)”.
-
La décima nota que revisaremos (CVSS 8,9) es de criticidad alta y trata sobre “Multiple vulnerabilities in Application Server ABAP of SAP NetWeaver and ABAP Platform”.
-
La undécima nota que revisaremos (CVSS 8,2) es de criticidad alta y trata sobre “Memory Corruption Vulnerability in SAP NetWeaver (Internet Graphics Service)”.
-
La duodécima nota que revisaremos (CVSS 7,7) es de criticidad alta y trata sobre “Memory Corruption vulnerability in SAP Web Dispatcher”.
-
La decimotercera nota que revisaremos (CVSS 7,5) es de criticidad alta y trata sobre “Denial of Service (DoS) vulnerability in SAP NetWeaver Application Server ABAP (Internet Communication Manager) and SAP Web Dispatcher”.
-
La decimocuarta nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Memory Corruption vulnerability in SAP NetWeaver Application Server (SAP Message Server)”.
-
La decimoquinta nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Multiple Vulnerabilities in SAP NetWeaver (Internet Graphics Service)”.
-
La decimosexta nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Memory Corruption vulnerability in Application Server ABAP for SAP NetWeaver and ABAP Platform”.
-
La decimoséptima nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Information Disclosure in SAP NetWeaver (SAP Message Server)”.
-
La decimoctava nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Missing Authentication check in SAP NetWeaver AS Java EDM Application”.
-
La decimonovena nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Memory Corruption vulnerability in Application Server ABAP of SAP NetWeaver and ABAP Platform (SAP Message Server)”.
-
La vigésima nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Denial of Service vulnerability in SAP NetWeaver Application Server ABAP, ABAP Platform and SAP Web Dispatcher”.
-
La vigesimoprimera nota con la misma criticidad (CVSS 7,5) es de criticidad alta y trata sobre “Insufficient Input Validation in SAP Host Agent”.
-
La vigesimosegunda y última nota que revisaremos (CVSS 7,2) es de criticidad alta y trata sobre “Code Injection vulnerability in SAP ABAP Developer Tools (AMDP Data Preview)”.
Este mes el tipo más predominante ha sido “Memory Corruption vulnerability” (7/38 en el patch day, excluyendo GitHub).
En la gráfica podemos ver la clasificación de las notas de noviembre, además de la evolución y clasificación de los últimos 5 meses anteriores (solo las notas del Sec. Tuesday / Patch Day – by SAP):
Detalle completo
El detalle completo de las notas más relevantes es el siguiente (en inglés):
-
Memory Corruption Vulnerability in SAP NetWeaver AS ABAP (Internet Communication Manager) (3778530): SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker could send specially crafted network traffic to trigger a memory corruption condition in the affected functionality. Successful exploitation could allow the attacker to execute arbitrary code and fully compromise the system, resulting in a high impact on confidentiality, integrity and availability of the system. A temporary workaround is available. CVSS v3 Base Score 10,0/10 [CVE-2026-76964].
-
Memory Corruption vulnerability in SAP Web Dispatcher (3778556): SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker could send specially crafted network traffic to trigger a memory corruption condition in the affected functionality. Successful exploitation could allow the attacker to execute arbitrary code and fully compromise the system, resulting in a high impact on confidentiality, integrity and availability of the system. A temporary workaround is available. CVSS v3 Base Score 10,0/10 [CVE-2026-89126].
-
Broken Access Control in SAP Gateway (3798345): SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal application server. As a result an unauthenticated attacker with network access to the SAP Gateway could exploit this weakness to potentially perform unauthorized actions within the application environment, resulting in a high impact on the confidentiality, integrity, and availability of the affected system. CVSS v3 Base Score 10,0/10 [CVE-2026-89103].
-
Missing Authentication in SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider) (3849308): SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain configurations. An unauthenticated attacker could submit specially crafted data to bypass authentication and impersonate arbitrary users, including privileged accounts. Successful exploitation could cause a full system compromise, with the impact potentially extending to connected components and systems beyond the affected system. This results in a high impact on confidentiality, integrity, and availability of the application. CVSS v3 Base Score 10,0/10 [CVE-2026-120017].
-
Code Injection vulnerability in SAP NetWeaver Knowledge Management (XML Forms) (3809153): SAP NetWeaver Knowledge Management (XML Forms) does not sufficiently restrict the selection of XSL transformations processed by the affected functionality. Under certain conditions, an authenticated user with access to the affected functionality could cause an unauthorized XSL transformation to be processed, potentially leading to arbitrary code execution in the application context. Successful exploitation could impact the confidentiality, integrity, and availability of the application. A temporary workaround is available. CVSS v3 Base Score 9,9/10 [CVE-2026-109803].
-
OS Command Injection vulnerability in ABAP Application Server for SAP NetWeaver and ABAP Platform (3792735): SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality. An attacker with low privileges could invoke affected functionality to execute arbitrary operating system commands on the underlying host. Successful exploitation could impact resources beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability of the system. A temporary workaround is available. CVSS v3 Base Score 9,9/10 [CVE-2026-76965].
-
Missing authorization check in S4CRM (3834842): SAP NetWeaver does not perform necessary authorization checks and lacks sufficient input validation in certain remote-enabled functionality. An attacker with low privileges could send specially crafted input through a remote interface to inject and execute arbitrary code within the affected system. Successful exploitation could extend the attacker’s reach beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability. CVSS v3 Base Score 9,9/10 [CVE-2026-109795].
-
Cross-Site Request Forgery (CSRF) vulnerability in SAP Web Dispatcher and Internet Communication Manager (3804858): SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation in certain administrative functionality. In the context of Application Server ABAP and SAP Web Dispatcher, an unauthenticated attacker could trick a logged-on administrator into visiting a malicious link. Visiting the link could cause unintended actions in the administrator’s session. Successful exploitation could lead to a full compromise of the underlying operating system, resulting in a high impact on confidentiality, integrity, and availability. A temporary workaround is available. CVSS v3 Base Score 9,6/10 [CVE-2026-89119].
-
XML External Entity (XXE) Vulnerability in SAP BusinessObjects Business Intelligence Platform (Web Intelligence) (3799117): SAP BusinessObjects Business Intelligence Platform (Web Intelligence) does not properly restrict external entity resolution when processing OLAP connection requests. An authenticated attacker could exploit this vulnerability to access restricted resources, enabling them to read sensitive files on the server and reach internal systems that are not otherwise exposed, impacting resources beyond the vulnerable component, resulting in a high impact on confidentiality and a low impact on both integrity and availability. CVSS v3 Base Score 9,1/10 [CVE-2026-109798].
-
Multiple vulnerabilities in Application Server ABAP of SAP NetWeaver and ABAP Platform (3769130): Due to improper RFC protocol validation in the SAP Kernel used by the Application Server ABAP of SAP NetWeaver and ABAP Platform, an unauthenticated attacker can send a crafted RFC request that exploits logical errors in memory management, leading to memory corruption. This could lead to a high impact on confidentiality and integrity with low impact on availability of the application. CVSS v3 Base Score 8,9/10 [CVE-2026-76966].
-
Memory Corruption Vulnerability in SAP NetWeaver (Internet Graphics Service) (3809953): SAP NetWeaver (Internet Graphics Service) does not sufficiently validate certain input values within incoming requests. An unauthenticated user could send a specially crafted request to trigger an out-of-bounds memory write in a worker process. Successful exploitation could result in memory corruption or repeated termination of the affected process, resulting in a high impact on availability and a low impact on integrity with no impact on confidentiality. CVSS v3 Base Score 8,2/10 [CVE-2026-120008].
-
Memory Corruption vulnerability in SAP Web Dispatcher (3803832): SAP Web Dispatcher does not sufficiently validate certain input. An unauthenticated attacker could send a specially crafted request causing memory corruption, resulting in a high impact on availability, with no impact on confidentiality and integrity. CVSS v3 Base Score 7,7/10 [CVE-2026-109800].
-
Denial of Service (DoS) vulnerability in SAP NetWeaver Application Server ABAP (Internet Communication Manager) and SAP Web Dispatcher (3808627): SAP NetWeaver Application Server ABAP and SAP Web Dispatcher do not sufficiently validate certain header values processed during inbound request handling. An unauthenticated attacker could send a specially crafted request to cause the affected process to become unavailable. This results in a high impact on availability. There is no impact on confidentiality and integrity. CVSS v3 Base Score 7,5/10 [CVE-2026-109793].
-
Memory Corruption vulnerability in SAP NetWeaver Application Server (SAP Message Server) (3805570): SAP NetWeaver Application Server (SAP Message Server) does not properly size memory allocations when handling certain HTTP requests. An unauthenticated attacker could send a specially crafted request to trigger a heap buffer overflow in affected functionality. Successful exploitation causes the component to abort and remain unavailable until it is restarted by the framework, resulting in a high impact on availability of the system. There is no impact on confidentiality and integrity of the application. CVSS v3 Base Score 7,5/10 [CVE-2026-120010].
-
Multiple Vulnerabilities in SAP NetWeaver (Internet Graphics Service) (3809934): This SAP security note addresses multiple vulnerabilities identified in SAP NetWeaver (Internet Graphics Service). Both Out-of-Bounds Read and Integer Overflow vulnerabilities are present due to insufficient validation of certain input values within incoming requests. An unauthenticated user could send specially crafted requests causing repeated termination of the worker process. This results in a high impact on availability with no impact on integrity or confidentiality. CVSS v3 Base Score 7,5/10 [CVE-2026-109806, CVE-2026-109807].
-
Memory Corruption vulnerability in Application Server ABAP for SAP NetWeaver and ABAP Platform (3792915): Due to a Memory Corruption vulnerability in Application Server ABAP for SAP NetWeaver and ABAP Platform, an unauthenticated attacker could send specially crafted requests to the application. If processed by the application, these requests could trigger a memory corruption condition in the parsing routine, which could cause the affected processes to crash and restart. By repeatedly sending such requests, the attacker could cause a sustained denial of service, leading to a high impact on availability. Confidentiality and integrity remain unaffected. CVSS v3 Base Score 7,5/10 [CVE-2026-76970].
-
Information Disclosure in SAP NetWeaver (SAP Message Server) (3808552): SAP Message Server does not properly handle certain malformed requests, which could be leveraged by an unauthenticated attacker to send specially crafted input. Successful exploitation could allow the attacker to retrieve sensitive information, resulting in a high impact on confidentiality. There is no impact on integrity and availability. CVSS v3 Base Score 7,5/10 [CVE-2026-109804].
-
Missing Authentication check in SAP NetWeaver AS Java EDM Application (3810485): SAP NetWeaver AS Java EDM Application does not perform an authentication check for certain web service requests. An unauthenticated attacker could send a specially crafted request to retrieve sensitive business information. This results in a high impact on confidentiality. There is no impact on integrity and availability. A temporary workaround is available. CVSS v3 Base Score 7,5/10 [CVE-2026-89114].
-
Memory Corruption vulnerability in Application Server ABAP of SAP NetWeaver and ABAP Platform (SAP Message Server) (3789273): Due to a Memory Corruption vulnerability in Application Server ABAP of SAP NetWeaver and ABAP Platform, an unauthenticated attacker could send specially crafted network requests to the affected service. By triggering the vulnerability, the attacker could cause the server to crash and disrupt active connections, leading to a denial of service condition. Successful exploitation could result in a high impact to the availability while the confidentiality and integrity remains unaffected. CVSS v3 Base Score 7,5/10 [CVE-2026-76973].
-
Denial of Service vulnerability in SAP NetWeaver Application Server ABAP, ABAP Platform and SAP Web Dispatcher (3805681): SAP NetWeaver Application Server ABAP, ABAP Platform, and SAP Web Dispatcher do not sufficiently handle resource consumption when processing certain requests. An unauthenticated attacker could send specially crafted requests to the affected component, causing excessive resource utilization and service disruption. This results in a high impact on availability. There is no impact on confidentiality and integrity. A temporary workaround is available. CVSS v3 Base Score 7,5/10 [CVE-2026-109794].
-
Insufficient Input Validation in SAP Host Agent (3842766): SAP Host Agent does not sufficiently validate certain inputs. Under certain condition, an attacker with low privileges could abuse the affected functionality to influence an internal component into loading a malicious file under a privileged account. Successful exploitation could lead to persistent code execution, resulting in a high impact on confidentiality, integrity and availability. CVSS v3 Base Score 7,5/10 [CVE-2026-120015].
-
Code Injection vulnerability in SAP ABAP Developer Tools (AMDP Data Preview) (3833364): SAP ABAP Developer Tools (AMDP Data Preview) does not perform sufficient validation and authorization checks within certain affected functionality. An attacker with high privileges could submit specially crafted input to inject and execute arbitrary code on the system. Successful exploitation could allow the attacker to fully compromise the system, resulting in a high impact on confidentiality, integrity and availability. A temporary workaround is available. CVSS v3 Base Score 7,2/10 [CVE-2026-120009].
Enlaces de referencia
Referencias, en inglés de SAP y Onapsis:
Recursos afectados
El listado completo de los sistemas/componentes afectados es el siguiente:
-
SAP NetWeaver AS ABAP (Internet Communication Manager): KRNL64UC 7.53, KERNEL 7.53, 7.54, 7.77, 7.93, 9.16, 9.18, 9.20
-
SAP Web Dispatcher: HDB 2.00, KRNL64UC 7.53, WEBDISP 7.53, 7.54, 7.77, 7.93, 9.16, XS_ADVANCED_RUNTIME 1.00, SAP_EXTENDED_APP_SERVICES 1, KERNEL 7.53, 7.54, 7.77, 7.93, 9.16, 9.18, 9.20, 9.21
-
SAP Gateway: KRNL64NUC 7.22, 7.22EXT, KRNL64UC 7.22, 7.22EXT, 7.53, 8.04, KERNEL 7.22, 7.53, 7.54, 7.77, 7.93, 8.04, 9.16, 9.20, 9.21
-
SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider): SAP_BASIS 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 758, 816, 920, 921, 922
-
SAP NetWeaver Knowledge Management (XML Forms): KMC-CM 7.50
-
SAP NetWeaver and ABAP Platform: KRNL64NUC 7.22, 7.22EXT, KRNL64UC 7.22, 7.22EXT, 7.22EX2, 7.22EX3, 7.53, 7.54, 7.77, 7.93, 8.04, 9.16, 9.18, 9.20, 9.21, KERNEL 7.22, 7.53, 7.54, 7.77, 7.93, 8.04, 9.16, 9.18, 9.20, 9.21
-
S4CRM: S4CRM 204, 205, 206, S4CEXT 107, 108, 109, BBPCRM 713, 714
-
SAP Web Dispatcher and Internet Communication Manager: WEBDISP 7.93, 9.16, XS_ADVANCED_RUNTIME 1.00, KERNEL 7.93, 9.16, 9.20, 9.21
-
SAP BusinessObjects Business Intelligence Platform (Web Intelligence): ENTERPRISE 430, 2025, 2027
-
SAP NetWeaver (Internet Graphics Service): BC-FES-IGS 7.20EXT, 7.20_EX2, 7.53, 7.54, 7.81, 9.16
-
SAP NetWeaver Application Server (SAP Message Server): KRNL64NUC 7.22, 7.22EXT, KRNL64UC 7.22, 7.22EXT, 7.53, 8.04, KERNEL 7.22, 7.53, 7.54, 7.77, 7.93, 8.04, 9.16, 9.18, 9.20, 9.21
-
SAP NetWeaver AS Java EDM Application: CE-RA-EDM 7.50
-
SAP NetWeaver Application Server ABAP, ABAP Platform and SAP Web Dispatcher: WEBDISP 7.77, 7.93, 9.16, XS_ADVANCED_RUNTIME 1.0, KERNEL 7.77, 7.93, 9.16
-
SAP Host Agent: SAPHOSTAGENT 7.22
-
SAP ABAP Developer Tools (AMDP Data Preview): SAP_BASIS 740, 750, 751, 752, 753, 754, 755, 756, 757, 758, 816, 920